Understanding Consent Messages
Consent messages emerged primarily as a compliance response to privacy legislation.
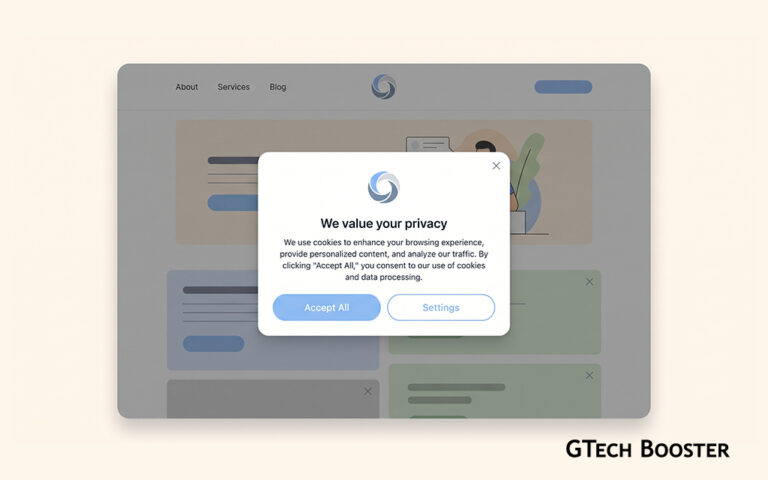
A consent message, sometimes called a consent banner, a cookie notice, or a privacy prompt, is the dialog that appears when a person first visits a website or opens an app, asking them to agree to, decline, or customize how their personal data is collected and used, most commonly for advertising, analytics, and other tracking purposes. What looks like a simple pop up is actually the visible front end of a much larger technical and legal system, involving privacy law, industry standards bodies, and platform specific certification requirements from companies like Google. This account examines consent messages in full: why they exist, the legal frameworks behind them, the technical infrastructure that powers them, the specific structure of two option and three option consent messages, the role and requirements of Google Certified Consent Management Platforms, and the broader debates and challenges surrounding consent design today.
Why Consent Messages Exist
The Legal Foundation
Consent messages emerged primarily as a compliance response to privacy legislation, most notably the European Union’s ePrivacy Directive, which requires informed consent before storing or accessing information on a user’s device such as cookies, and the General Data Protection Regulation, which sets a broader standard for lawful processing of personal data, including a requirement that consent be freely given, specific, informed, and unambiguous. Similar obligations have since appeared in other jurisdictions, including the United Kingdom’s data protection framework, Switzerland’s revised data protection law, and a growing patchwork of state level privacy laws in the United States, such as the California Consumer Privacy Act and its successor legislation, each of which imposes its own specific requirements around disclosure, opt out rights, and in some cases affirmative consent for the sale or sharing of personal data.
What a Consent Message Is Actually Asking
Functionally, a consent message is asking a visitor to make a decision, or a series of decisions, about specific categories of data processing, most commonly the storage of cookies or similar identifiers on their device, and the use of that stored information for purposes such as basic site functionality, analytics and measurement, advertising personalization, and sharing data with third party advertising partners. Behind the scenes, this decision is translated into a technical consent signal that other systems on the page, and often third party advertising and analytics vendors, can read and respect before they load their own tracking code or begin processing personal data.
The Technical Architecture Behind a Consent Message
The Consent Management Platform
The software responsible for displaying a consent message, capturing a visitor’s choices, storing those choices, and communicating them to other systems on the page is called a consent management platform, universally abbreviated as a CMP. A CMP typically loads before any other tracking or advertising script on a page, checks whether the visitor has already made a choice, displays the consent message if no valid choice is on record, and then sets the appropriate technical signals once a choice is made, so that other scripts on the page know whether they are permitted to run and what they are permitted to do.
The IAB Transparency and Consent Framework
Much of the modern consent ecosystem, particularly for advertising, is built around the Transparency and Consent Framework, a technical and policy standard maintained by IAB Europe, the regional trade body for the digital advertising industry. Under this framework, a CMP that has registered with IAB Europe generates what is called a Transparency and Consent string, commonly called a TC string, a compact encoded piece of text that records exactly which purposes and which specific advertising vendors a visitor has consented to. This string is then made available to other systems on the page, including advertising exchanges and demand side platforms, which are expected to read and respect it before processing that visitor’s data for advertising purposes. The framework standardizes not just the technical string format but also a defined list of legal purposes, such as storing information on a device, using profiles to select personalized advertising, or measuring advertising performance, giving the entire advertising ecosystem a shared vocabulary for what a given consent choice actually covers.
Google Consent Mode
Separately from, but closely integrated with, the IAB framework, Google operates its own signaling system called Consent Mode, which allows a website to communicate a visitor’s consent status directly to Google’s own tags, including Google Analytics, Google Ads, and other Google marketing tags, so that those tags can adjust their own behavior accordingly rather than firing indiscriminately regardless of consent status. Consent Mode version two, the current standard, introduced two additional signal parameters, covering the use of user data for advertising purposes and the use of that data for ad personalization specifically, alongside the original signals governing analytics storage and advertising storage. A properly configured CMP must set these signals correctly, defaulting typically to a denied state before a visitor has made any choice, and updating them accurately once a choice has been recorded, since default behavior is one of the specific things Google evaluates when certifying a CMP.
The Structure of a Consent Message
Screens Within a Single Message
A modern consent message is rarely just a single static pop up with one decision to make. Instead, it is typically composed of multiple linked screens that a visitor can move between depending on which buttons or links they choose to interact with. The most common structure includes a main consent screen shown first, a manage your data screen that lists the specific purposes being requested, and, beneath that, a further screen listing the specific individual advertising vendors or partners requesting consent, allowing a visitor to drill down from a broad overall decision to fine grained, vendor by vendor control if they choose to.
Two Choice Consent Messages
A two choice, or two button, consent message presents a visitor with exactly two primary actions on its main screen: a clearly labeled consent button, and a manage options link rather than a separate, equally prominent decline button. Clicking the consent button grants consent to all of the purposes and vendors configured for that message and closes the dialog immediately. Clicking manage options instead opens a secondary manage your data screen, where every individual purpose being requested is displayed, deselected by default, and the visitor is given a choice between an accept all button, which behaves identically to clicking consent on the main screen, and a confirm choices button, which accepts only whatever specific purposes the visitor has actively selected on that screen, leaving unselected purposes unconsented. From that manage your data screen, a visitor can typically drill down one level further into a vendor preferences screen, listing the individual named advertising and data partners requesting consent or disclosing a legitimate interest basis for processing, again defaulted to deselected, with its own accept all and confirm choices options. In a two choice design, there is no dedicated, single click decline or do not consent button sitting directly alongside the consent button on the very first screen a visitor sees. A visitor wishing to decline entirely must click through to the manage options screen and either leave every purpose deselected or actively deselect them before confirming their choices.
Three Choice Consent Messages
A three choice, or three button, consent message adds one additional element directly to the main screen: a distinct do not consent button, sitting alongside the consent button, so that a visitor can decline all of the requested purposes and vendors in a single click without needing to navigate to a secondary screen first. Beyond this addition, the underlying structure mirrors the two choice design closely. The main screen still includes a manage options link leading to the same manage your data screen, which in turn leads to the same vendor preferences screen, each retaining their own accept all and confirm choices controls, with all individual purposes and vendors still defaulted to deselected. The presence of an immediately visible, equally prominent do not consent button is the defining and meaningful difference between the two formats, since it changes how many steps a visitor must take to decline consent altogether, from at minimum two interactions in a two choice design, opening manage options and then confirming an empty or fully deselected set of choices, down to a single click in a three choice design.
Button Copy Requirements
Regardless of which format is used, the specific wording used for the affirmative consent action is not left entirely to a publisher’s discretion. Under IAB Transparency and Consent Framework policy requirements that Google’s own consent message tooling enforces, the button that grants consent must use language that communicates a clear, affirmative choice, with wording along the lines of an explicit statement of consent considered acceptable, while vague or misleading phrasing that merely implies moving forward with the site, without actually communicating that a consent decision is being made, is not considered acceptable under the framework’s rules.
Choosing Between Two and Three Choice Formats
Regulatory Pressure Toward Symmetry
The choice between a two option and a three option consent message is not purely a design or business preference. European data protection regulators and the European Data Protection Board have repeatedly emphasized that where a consent interface offers an easy, one click path to accept, it should generally offer an equally easy, equally prominent path to refuse, on the reasoning that consent obtained through a design that makes acceptance meaningfully easier than refusal is not genuinely free and informed as required under data protection law. This regulatory expectation has been a significant driver behind the move toward three choice, equally weighted accept and decline designs in many jurisdictions and for many publishers operating under European or UK data protection law, even though Google’s own tooling continues to support the two choice format as a configurable option as well.
Business and User Experience Trade-offs
From a publisher’s perspective, the choice between formats involves real trade-offs beyond pure legal risk tolerance. A two choice design, without an immediately visible decline button, has historically tended to produce a higher rate of full consent, since some portion of visitors who might have declined if given an equally easy option will instead simply click the prominent consent button rather than navigating to a secondary screen to decline. A three choice design, by contrast, generally produces a more balanced mix of outcomes, including a higher proportion of visitors declining outright, but is viewed by many privacy focused regulators, advocacy groups, and increasingly by publishers themselves as a more defensible and user respecting approach, reducing the legal and reputational risk associated with what regulators sometimes describe as a design pattern that nudges users toward consent rather than presenting a genuinely neutral choice.
Per Country Configuration
Google’s own consent messaging tools allow the choice between two and three button formats, along with other message settings, to be configured on a country by country basis rather than applied uniformly across every visitor worldwide, allowing a publisher to align its message format with the specific regulatory expectations of each region its visitors are located in, since legal expectations and enforcement posture around consent design are not identical across every jurisdiction a global publisher might serve.
Google Certified Consent Management Platforms
The Certification Requirement
Google requires that publishers using its advertising products, including Google AdSense, Google Ad Manager, and Google AdMob, use a consent management platform that has been specifically certified by Google and that integrates with the IAB Transparency and Consent Framework, whenever those publishers intend to serve personalized advertising to users located in the European Economic Area, the United Kingdom, or Switzerland. This requirement became mandatory for the European Economic Area and the United Kingdom in January 2024, with Switzerland following in mid-2024. Publishers who do not use a certified, TCF integrated CMP for these regions are restricted to serving only limited or non-personalized advertising to affected visitors, which typically generates substantially lower advertising revenue than personalized advertising.
What Google Evaluates During Certification
Achieving Google Certified CMP status involves meeting a defined set of technical and policy requirements that Google reviews before granting certification. These generally include formal registration as a member of the IAB Europe Transparency and Consent Framework and the ability to correctly generate standards compliant TC strings, correct implementation of Google Consent Mode, including all of the required signal parameters, proper default consent behavior, meaning that no tags are permitted to fire with a granted consent state before a visitor has actually made a choice, genuine user choice in the interface design itself, meaning the consent message must present an actual, meaningful decision rather than a design that effectively forces or heavily steers a particular outcome, and transparent, auditable storage of consent records so that a visitor’s recorded choice can be verified and is not silently ignored or overwritten.
The List of Certified CMPs
Google maintains and periodically updates a public list of third party CMPs that have achieved certification, alongside its own first party CMP tooling built directly into Ad Manager, AdSense, and AdMob’s Privacy and messaging features. This list includes a range of established consent management vendors serving publishers of different sizes and technical sophistication, and Google encourages publishers to review this list directly and periodically, since certification status, available features, and specific vendors on the list can change over time as Google continues to evaluate and re-certify CMPs against evolving requirements, including the ongoing transition across the industry from earlier versions of the IAB framework to newer ones.
Choosing Between Google’s Own CMP and a Third Party CMP
Publishers using Google’s advertising products are not required to use Google’s own first party CMP tooling specifically, so long as whichever CMP they do use is certified and properly integrated with the IAB framework and Google Consent Mode. Google’s own guidance to publishers explicitly frames this as an open choice, encouraging publishers to weigh their own specific needs, technical resources, and preferences, since third party CMPs often offer additional features, broader customization, or support for a wider range of non-Google advertising and analytics vendors beyond what Google’s own built in tooling is specifically designed to manage.
The Broader Consent Message Ecosystem
Beyond Advertising: Analytics and Functional Cookies
While advertising consent tends to attract the most regulatory and industry attention, a properly implemented consent message generally governs several distinct categories of data processing, commonly including strictly necessary or functional cookies that are exempt from consent requirements because they are essential to basic site operation, analytics or performance related storage used to measure site usage and behavior, and personalization or advertising related storage used for the kinds of targeted advertising purposes described earlier in this account. A well designed consent message clearly separates these categories so a visitor can make distinct, informed choices about each rather than facing only a single undifferentiated accept or decline decision covering every possible use of their data at once.
Legitimate Interest as an Alternative Legal Basis
Not every purpose disclosed in a consent message is necessarily presented as requiring affirmative opt in consent. Under the IAB framework and the underlying data protection law it is built upon, certain purposes may instead be disclosed to a visitor on the basis of a publisher’s legitimate interest, a distinct legal basis that does not require affirmative consent but does require that the visitor be clearly informed and given a straightforward way to object or opt out. Consent messages built to the IAB framework generally surface both categories together on the manage your data screen, showing which purposes are being requested on a consent basis and which are being disclosed on a legitimate interest basis, each with its own corresponding way for the visitor to accept or object.
Consent Persistence and Renewal
Once a visitor makes a choice through a consent message, that choice is generally stored, commonly in a first party cookie or similar local storage mechanism, and referenced on subsequent visits so the message does not need to be shown again unless specific conditions are met. These conditions typically include the underlying consent record expiring after a defined period, a publisher making a material change to the purposes or vendors covered by the message, or a publisher deliberately triggering a fresh consent collection cycle, for example to comply with an updated privacy policy or a change in applicable law.
Common Criticisms and Ongoing Debates
Consent Fatigue
One of the most widely discussed criticisms of the modern consent message ecosystem is what is often called consent fatigue, the tendency of users, after repeatedly encountering similar looking consent dialogs across countless different websites, to click through them quickly and often without genuinely reading or considering the choice being presented, frequently defaulting to whichever option is fastest or most prominent regardless of their actual underlying privacy preference. Critics argue this undermines the entire premise of informed, freely given consent that the underlying legal frameworks were designed to protect.
Dark Patterns and Regulatory Scrutiny
Regulators and consumer advocacy groups have specifically scrutinized consent message designs that make declining meaningfully more difficult or time consuming than accepting, sometimes described using the broader term dark patterns, referring to interface designs deliberately or effectively structured to steer users toward a particular outcome rather than presenting a neutral choice. This scrutiny has directly influenced the industry wide movement toward three choice, symmetrically weighted consent and decline options described earlier in this account, and continues to shape ongoing guidance and enforcement activity from data protection authorities across multiple jurisdictions.
Emerging Alternatives and Signals
Beyond the per site consent message model, alternative and complementary approaches have continued to develop, including browser or device level global privacy signals that a user can set once and have automatically communicated to every site they visit, intended to reduce the need to repeatedly make the same consent decision on every individual website. Integration of these broader signals alongside traditional per site consent messages remains an active and evolving area, with CMPs and advertising platforms, including Google, continuing to adapt their own requirements and supported signal types as this landscape develops further.
Guiding continental document
Africa
African Union
- African Union Convention on Cyber Security and Personal Data Protection (the Malabo Convention), adopted 27 June 2014, entered into force 8 June 2023. This is the only binding continent-wide treaty on data protection outside Europe.
https://au.int/en/treaties/african-union-convention-cyber-security-and-personal-data-protection
Economic Community of West African States (ECOWAS)
- ECOWAS Supplementary Act A/SA.1/01/10 on Personal Data Protection within ECOWAS, 2010, a binding regional instrument for West African member states, predating and partly informing the Malabo Convention.
East African Community (EAC)
- EAC Legal Framework for Cyberlaws, which includes model provisions and guidance on data protection for partner states, developed alongside UNCTAD.
Europe
European Union
- General Data Protection Regulation, Regulation (EU) 2016/679, the primary binding law governing personal data processing and consent across EU and EEA member states.
https://eur-lex.europa.eu/eli/reg/2016/679/oj - ePrivacy Directive, Directive 2002/58/EC as amended by Directive 2009/136/EC, the specific legal basis requiring consent for cookies and similar tracking technologies.
https://eur-lex.europa.eu/legal-content/EN/TXT/?uri=CELEX:32002L0058
Council of Europe (broader than the EU, covering 46 member states)
- Convention 108, and its modernized form Convention 108+, formally the Convention for the Protection of Individuals with regard to the Processing of Personal Data, the only legally binding international data protection treaty open to countries beyond Europe as well.
https://www.coe.int/en/web/data-protection/convention108-and-protocol - European Convention on Human Rights, Article 8, protecting the right to respect for private and family life, the foundational human rights basis underlying European data protection law.
https://www.echr.coe.int/documents/convention_eng.pdf
Asia
Association of Southeast Asian Nations (ASEAN)
- ASEAN Framework on Personal Data Protection, endorsed 2016, a non-binding set of common principles for member states.
https://asean.org/wp-content/uploads/2012/05/10-ASEAN-Framework-on-PDP.pdf - ASEAN Model Contractual Clauses for Cross Border Data Flows, 2021, non-binding template clauses for lawful cross-border transfers among member states.
Asia-Pacific Economic Cooperation (APEC), spanning Asia and the Pacific Rim
- APEC Privacy Framework, endorsed 2005, updated 2015, a non-binding set of privacy principles across the 21 APEC member economies.
https://www.apec.org/publications/2005/12/apec-privacy-framework - APEC Cross-Border Privacy Rules (CBPR) System, endorsed 2011, a voluntary accountability-based certification system for cross-border data flows.
https://www.apec.org/about-us/about-apec/fact-sheets/what-is-the-cross-border-privacy-rules-system
The Americas
Organization of American States (OAS)
- Updated Principles on Privacy and Data Protection, prepared by the OAS Inter-American Juridical Committee, a non-binding set of hemispheric principles for member states across North, Central, and South America and the Caribbean.
http://www.oas.org/en/sla/dil/
Ibero-American Data Protection Network (RIPD), covering Latin America, Spain, Portugal, and Andorra
- Standards for Personal Data Protection for the Ibero-American States, first approved 2017, updated 2026, a regional reference model for national legislation and cross-border data transfer standard contractual clauses.
https://www.redipd.org
Caribbean Community (CARICOM)
- CARICOM has circulated model data protection legislation and harmonization guidance for member states, though it has not adopted a single binding regional data protection treaty comparable to the EU or Malabo instruments; most Caribbean states legislate individually, often informed by CARICOM model bills.
Oceania
There is no single binding continental data protection treaty for Oceania comparable to the EU or the Malabo Convention. Coverage instead comes through overlapping bodies:
- Several Pacific and Oceanian economies, including Australia and Papua New Guinea, participate in the APEC Privacy Framework and CBPR system listed above.
- The Pacific Islands Forum has issued non-binding digital and ICT governance guidance touching on data protection as part of broader regional digital strategy work, but without a dedicated binding privacy convention.
Global and Cross-Continental Standards
- OECD Guidelines Governing the Protection of Privacy and Transborder Flows of Personal Data, originally 1980, revised 2013, an influential non-binding standard that shaped most of the regional frameworks above.
https://www.oecd.org/en/publications/oecd-guidelines-on-the-protection-of-privacy-and-transborder-flows-of-personal-data_9789264196391-en.html - United Nations Guidelines for the Regulation of Computerized Personal Data Files, adopted by the UN General Assembly, 1990.
Antarctica
Antarctica has no permanent population or national jurisdiction and is governed by the Antarctic Treaty System rather than any data protection framework; no continental consent or privacy instrument exists for it.
Wrapping Up
A consent message is far more than a simple pop up asking permission to use cookies. It sits atop a substantial technical and legal infrastructure, involving specific data protection law, the IAB Transparency and Consent Framework’s standardized purposes and TC string format, Google’s own Consent Mode signaling system, and a formal certification process that platforms like Google require publishers to satisfy before they are permitted to serve personalized advertising in key regulated markets. The structural choice between a two option message, which channels a visitor toward a prominent consent action with decline available only after navigating to a secondary screen, and a three option message, which places an equally prominent decline option directly alongside consent on the very first screen, is not a minor cosmetic detail but a decision with real implications for regulatory compliance, user trust, and advertising revenue. Google Certified Consent Management Platforms exist specifically to ensure that whichever format and configuration a publisher ultimately chooses, the underlying technical signals, default behaviors, and genuine availability of choice meet a consistent, auditable standard across an advertising ecosystem that spans countless publishers, vendors, and jurisdictions. As privacy law and industry standards continue to evolve, the specific design and mechanics of consent messages are likely to keep changing, but the underlying goal they are built to serve, giving people a genuine, informed choice over how their data is used, remains the constant thread running through all of it.
More Information ℹ
- https://au.int/en/treaties/african-union-convention-cyber-security-and-personal-data-protection
- https://eur-lex.europa.eu/eli/reg/2016/679/oj
- https://eur-lex.europa.eu/legal-content/EN/TXT/?uri=CELEX:32002L0058
- https://www.coe.int/en/web/data-protection/convention108-and-protocol
- https://www.echr.coe.int/documents/convention_eng.pdf
- https://asean.org/wp-content/uploads/2012/05/10-ASEAN-Framework-on-PDP.pdf
- https://www.apec.org/publications/2005/12/apec-privacy-framework
- https://www.apec.org/about-us/about-apec/fact-sheets/what-is-the-cross-border-privacy-rules-system
- http://www.oas.org/en/sla/dil/
- https://www.redipd.org
- https://www.oecd.org/en/publications/oecd-guidelines-on-the-protection-of-privacy-and-transborder-flows-of-personal-data_9789264196391-en.html

Conversation
Login to comment.
Log In / Register